Ahmad Rafi Sutanto/

DECONSTRUCTINGTHE UNSEENSYSTEMS

Undergraduate researcher and defensive security engineer focused on digital forensics, proactive threat detection, and resilient system infrastructure.

Digital Forensics & DFIRBlue Team OperationsPETIR Cyber SecurityCSC BINUS Deputy Coordinator R&DCI/CD & DevOps Automation
DISCOVER
STATUS: Open to Blue Team, SOC & DFIR Opportunities

WHOAMI

Breaking systems to defend them, Tracing forensic anomalies to reveal ground truth

I'm Ahmad Rafi Sutanto, a Cybersecurity undergraduate at BINUS University specializing in Blue Team operations, Digital Forensics, and Threat Detection.

Currently serving as Deputy Coordinator of R&D at Cyber Security Community (CSC) and Apprentice at PETIR Cyber Security, where I architect automated CI/CD security infrastructure, orchestrate competition problem sets, and dissect low-level kernel and memory telemetry.

0.00Cumulative GPA / 4.00
0CTF Challenges Orchestrated
0+Challenge Authors Led
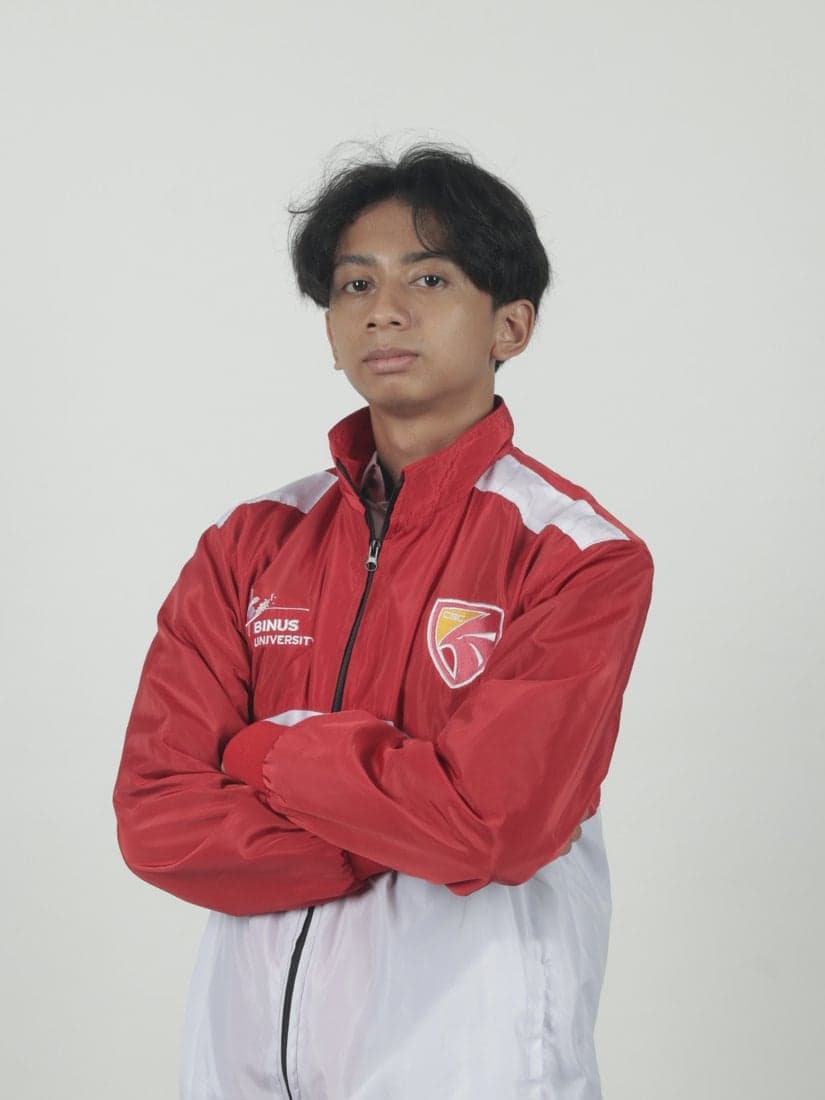
Ahmad Rafi Sutanto — Portrait
Forensic Investigation Workstation
CSC BINUS R&D and PETIR CTF Sessions

Ahmad Rafi Sutanto

CERTIFICATIONS & CREDENTIALS
Verified achievements & professional candidate tracks
Security Blue Team — Blue Team Level 1 (BTL1) Badge
Active Pursuit

Security Blue Team — Blue Team Level 1 (BTL1)

Security Blue Team·Currently Preparing

24-hour practical incident response exam: network PCAP triage, digital forensics, SIEM threat hunting, and malware analysis.

W
Verified

Wreck-IT 7.0 — Finalis General Capture The Flag

Politeknik Siber dan Sandi Negara (Poltek SSN / BSSN)·05 Agustus 2026

National cyber competition finalist credential awarded to Tim HM Plenger (Ahmad Rafi Sutanto) for outstanding defense operations and incident triage problem solving.

TECHNICAL TOOLKIT & CAPABILITIES

SPECIALIST ARSENAL& OPERATIONAL TOOLKIT

Digital ForensicsDFIR & REVERSING

DFIR & Reverse Engineering

Dead-box & volatile memory triage, filesystem artifact parsing, timeline reconstruction, and evidence correlation.

ACTIVE DFIR & REVERSING WORKBENCH (10 TOOLS)
Volatility 3
Memory Forensics & Triage
Autopsy
Dead-Box Disk Forensics
FTK Imager
Raw E01 Evidence Carving
Eric Zimmerman Tools
Windows Artifact Triage ($MFT)
Ghidra
Static Disassembly & Decompilation
x64dbg
Dynamic Binary Debugging
JADX
Android DEX & APK Decompiler
APKTool
Mobile App Disassembly
Wireshark
Packet & Protocol Inspection
ELF & Extended Attributes
Linux Binary & xattr Analysis
Blue TeamTHREAT DETECTION & DEFENSE

Threat Detection & Defensive Ops

Security operations, log telemetry analysis, threat hunting, application proxying, and containerized defense.

ACTIVE BLUE TEAM & INFRASTRUCTURE ARSENAL (10 TOOLS)
Splunk SIEM
Threat Hunting & Log Search
Sysmon Telemetry
Host Activity & Network Monitor
Windows Event Logs (EVTX)
Security & Logon Auditing
Burp Suite
Web Proxy & Traffic Triage
YARA Rules
Malware Signature Detection
Sigma Rules
Detection as Code & SIEM Rules
Linux
Systems Hardening & systemd
Docker
Container Isolation & Sandboxing
CI/CD (GitHub Actions)
Automated Deployment Pipelines
Git
Version Control & Integrity Audit

SELECTED WORK

SELECTEDPROJECTS & BUILDS

FEATURED INFRASTRUCTUREDevOps · Competition Infrastructure · 2026
CSC CTF Contest 2026

CSC CTF Contest 2026 · Automated CI/CD Platform

End-to-end automated deployment pipeline and competition architecture for 30 challenges across 6 categories.

79 PRs Merged · 128/285 Commits (45%): End-to-end automated CI/CD pipeline via GitHub Actions, ctfcli, and Docker on VPS.
GitHub ActionsDockerctfcliPython
DIGITAL FORENSICSBEECTF · 2026
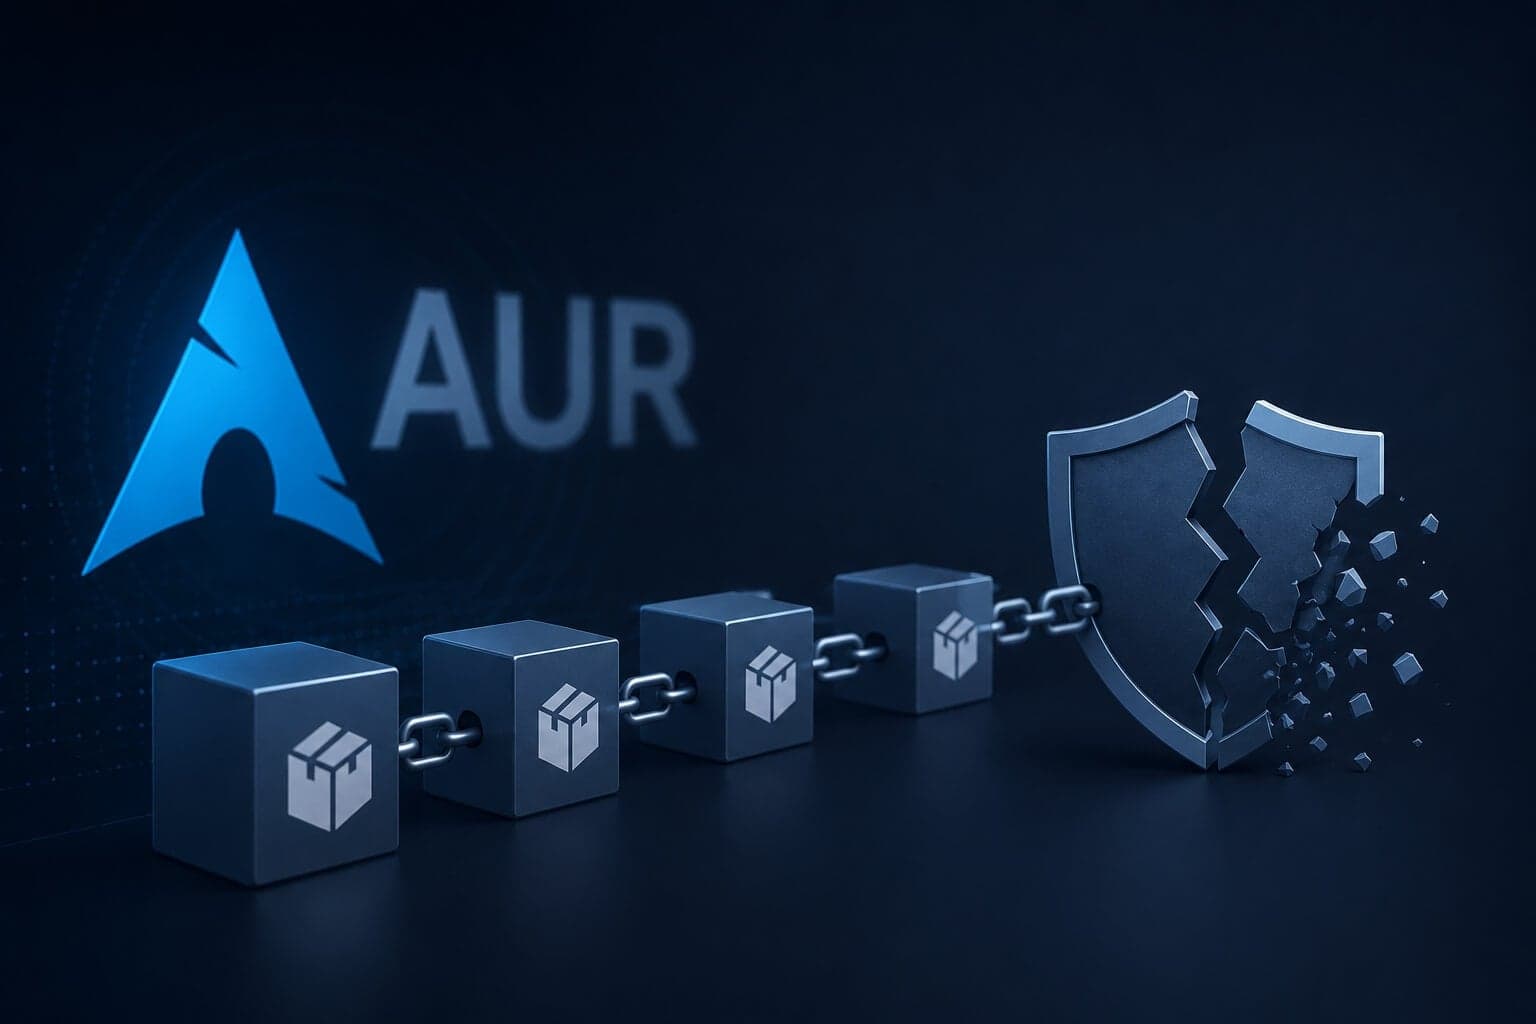
The Poisoned AUR

The Poisoned AUR · BeeCTF Forensics Challenge

Simulated real-world Arch Linux compromise via malicious AUR package with multi-layer forensic trails.

BeeCTF 2026: Multi-layer trail across ALPM logs, systemd, ELF headers & xattr.
Linux Forensicssystemd JournalELF Analysis
REPO

EXPERIENCES & FIELD LOGS

Aug 2026 · 1 moSumedang & Bandung, Jawa Barat · Remote
PETIR Cyber Security Logo

Challenge Author (Digital Forensics)

PETIR Cyber Security· IFEST 2026 (Universitas Padjadjaran)

Commissioned as external Digital Forensics challenge author for IFEST 2026 (HIMATIF Universitas Padjadjaran) via PETIR Cyber Security consultancy.

  • Developed 'Dead Box' forensics challenge simulating LUKS volume encryption, ext4 unallocated artifact carving, and hidden keyfile extraction.
  • Synthesized multi-stage attack scenarios across Linux PAM logs, Git object zlib streams, and binary reversing triage.
  • Delivered official reference writeup and automated validation solver harness to guarantee competition integrity.
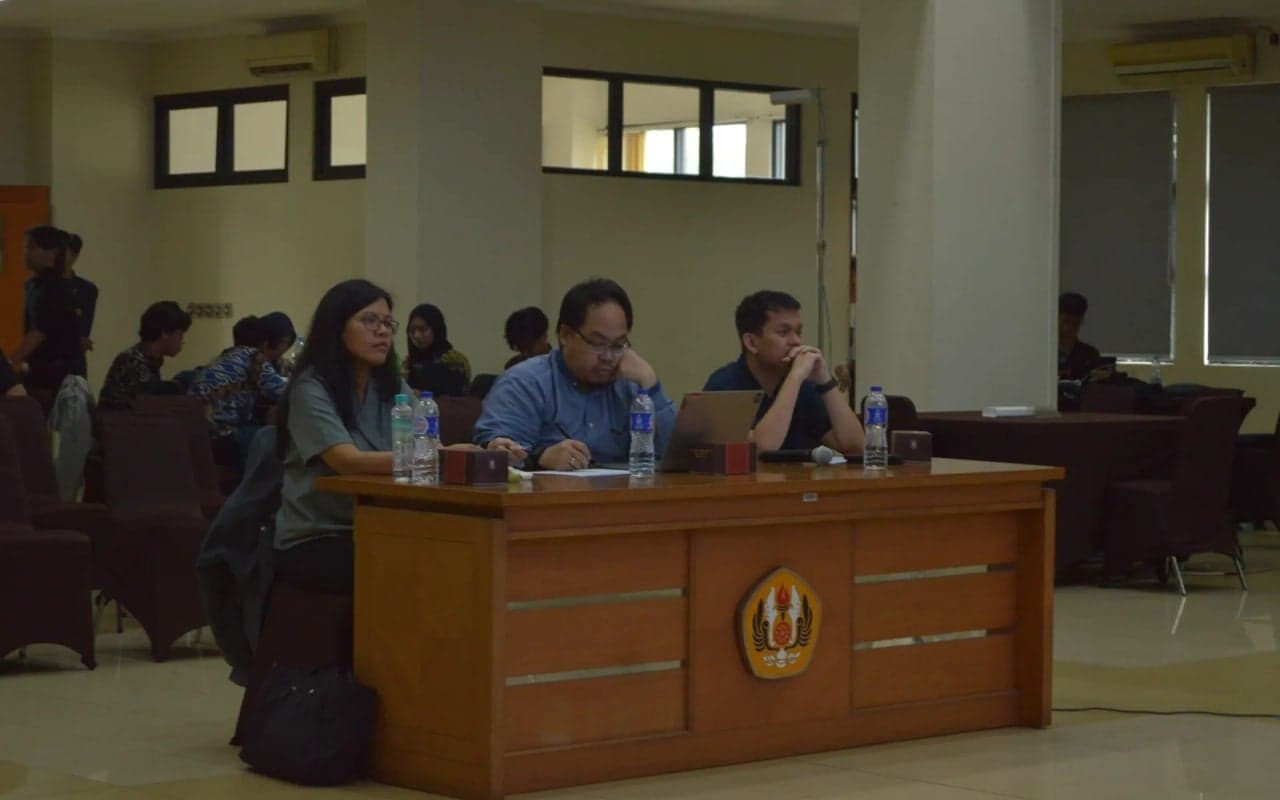
IFEST 2026 — Universitas Padjadjaran CTF Competition

IFEST 2026 CTF Competition — HIMATIF Universitas Padjadjaran

IFEST 2026 — Universitas Padjadjaran CTF Competition
Aug 2026 · 1 moWest Jakarta, Jakarta, Indonesia
PETIR Cyber Security Logo

Challenge Author (Digital Forensics)

PETIR Cyber Security· BeeCTF 2026 (Beefest)

Authored 'The Poisoned AUR' digital forensics challenge simulating an Arch Linux package compromise.

  • Synthesized multi-layered evidence across package logs, shell history, systemd, ELF, and xattr.
  • Authored official writeup covering command-line (WSL2) and GUI (FTK Imager) investigation paths.
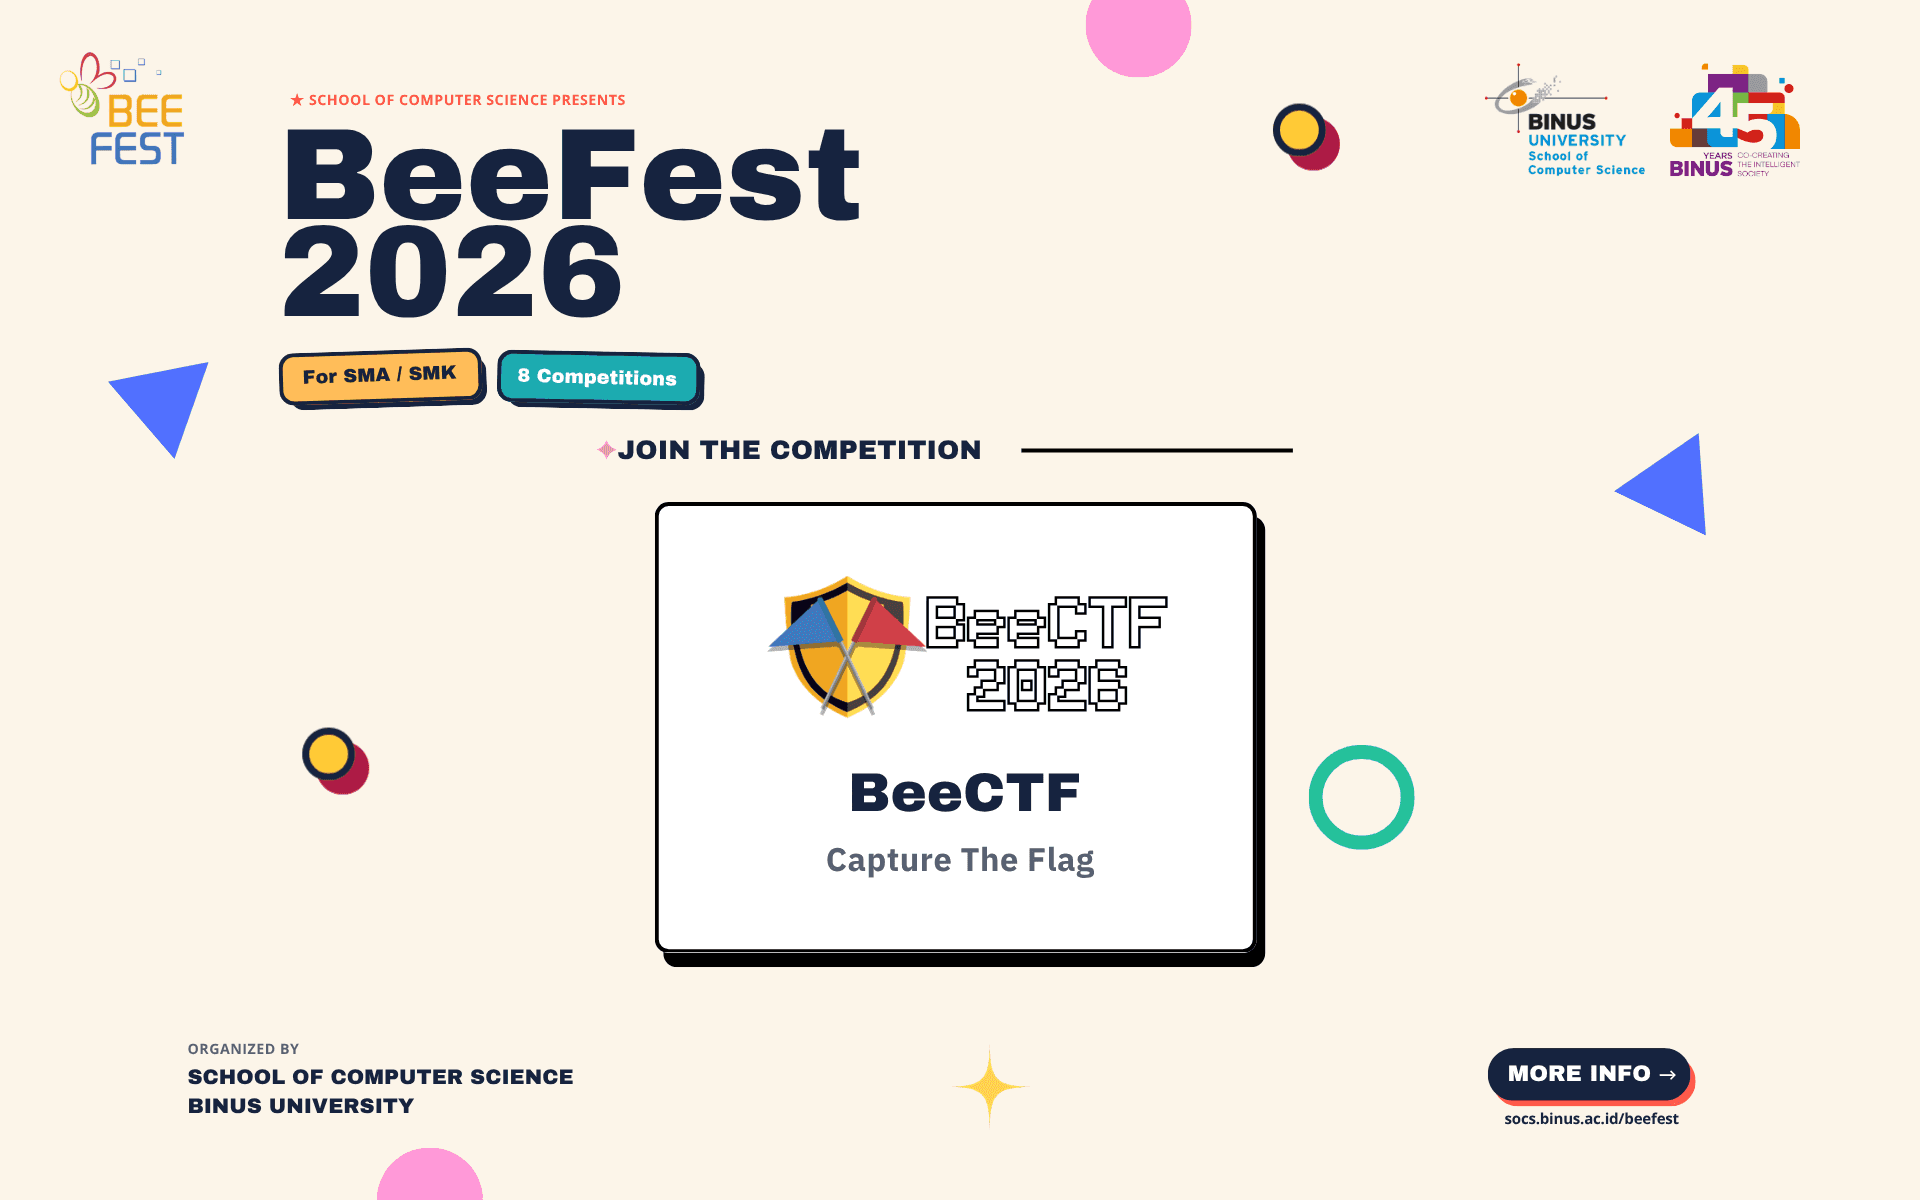
BEE Capture The Flag — Official Competition Banner
The Poisoned AUR — Forensic Challenge Scenario
01 / 02

BeeFest BeeCTF Competition — School of Computer Science BINUS University

BEE Capture The Flag — Official Competition Banner

CTF WRITEUPS& FIELD ARCHIVES

Curated competition field reports, digital forensics investigations, and security challenge walkthroughs from national tournaments.

3.4 MB PDF2025
Kemendikbudristek · Host: UNNES

GEMASTIK CTF

National ICT Competition — Cybersecurity Division

National tournament field report with Team PETIR Stand by Me: solutions across web exploitation, cryptography, and digital forensics triage.

GEMASTIKPuspresnasUNNESForensicsWeb Security
5.2 MB PDF2025
Universitas Gadjah Mada (UGM)

FindIT! CTF

National Cybersecurity Competition

National competition field report covering digital forensics triage, web exploitation, and reverse engineering problem sets.

UGMFindIT!Digital ForensicsWeb Security
1.0 MB PDF2025
Politeknik Siber dan Sandi Negara (Poltek SSN / BSSN)

Wreck-IT CTF

National Cyber Defense Competition

Defense operations and incident triage report with Team HM Plenger: packet inspection, vulnerability dissection, and host forensics.

Poltek SSNBSSNDefense TriagePacket Analysis
8.1 MB PDF2026
PETIR Cyber Security · BINUS University

PETIR REGEN26

Internal Qualification Tournament

Internal candidate qualification report for PETIR BINUS covering disk forensics, network packet dissection, and binary exploitation.

Internal QualificationPETIR BINUSDigital ForensicsPwn

GET IN TOUCH & DISPATCH

LET'S UNCOVER
WHAT'S HIDDEN

Research collaborations, forensic tooling, CTF challenge authoring: my inbox is open.